Imagine this: You’re a highly skilled cybersecurity professional, hired to test the very defenses meant to protect critical infrastructure. You’ve got all the paperwork, all the authorizations, and a clear set of rules. You’re doing your job, playing the part of a sophisticated adversary to make the real world safer. Sounds like a noble mission, right?
Now, imagine that same scenario ending not with a handshake and a detailed report, but with handcuffs, a booking photo, and a trip to jail. Sound like a bad dream? For two dedicated penetration testers in Iowa, it was a terrifying reality that ultimately led to a staggering $600,000 settlement. This isn’t just a story about a security assessment; it’s a cautionary tale about misunderstanding, legal battles, and the crucial need for clear communication in the world of ethical hacking.
The Mission: A Crucial “Red Team” Exercise at an Iowa Courthouse
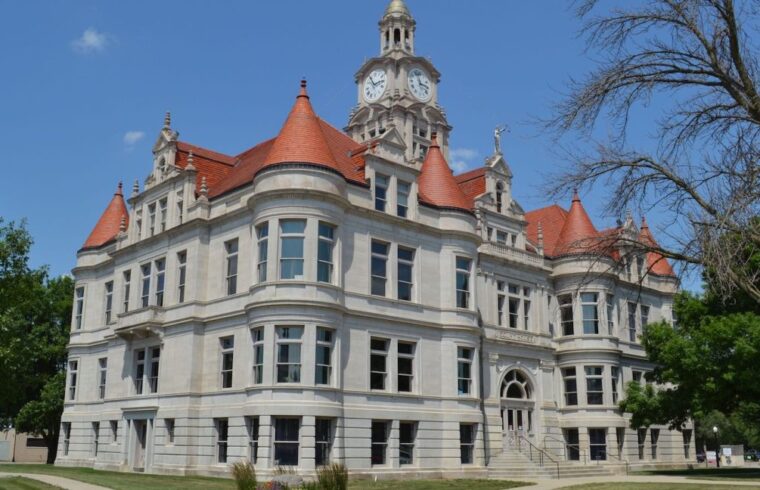
In 2019, Gary DeMercurio and Justin Wynn, two expert penetration testers working for the respected Colorado-based security firm Coalfire Labs, were tasked with a critical mission. Their objective? To perform a “red team” exercise on a county courthouse in Iowa. If you’re wondering what a red team exercise entails, let’s break it down.
What Exactly is a “Red Team” Exercise, Anyway?
Think of it like a highly realistic, full-scale dress rehearsal for a real-world attack. Unlike simpler vulnerability scans or basic penetration tests, red team exercises go deep. They involve security professionals mimicking the techniques, tactics, and procedures of actual criminal hackers, spies, or even physical burglars. The goal isn’t just to find vulnerabilities, but to test the organization’s entire security posture—people, processes, and technology—against persistent, sophisticated threats. It’s about asking: “Could a real attacker get in, and if so, how far could they go before being caught?”
DeMercurio and Wynn weren’t just probing firewalls from a remote location. Their engagement explicitly included physical attacks. We’re talking about things like trying doors, bypassing locks (yes, even lockpicking!), and attempting to gain unauthorized access to physical spaces. The rules were clear: no significant damage was to be caused, but the boundaries of physical security were absolutely on the table. They had written authorization from the Iowa Judicial Branch itself, a crucial detail that makes their subsequent arrest even more perplexing.
Arrested for Doing Their Job: A Stunning Reversal
Despite their legitimate authorization and adherence to the agreed-upon rules of engagement, something went terribly wrong. While performing their authorized security assessment, Gary and Justin found themselves in a situation no ethical hacker ever anticipates: they were arrested. Can you imagine the shock? You’re performing a vital service, operating with official permission, and suddenly you’re treated like a criminal, as if you’d just walked into a hornet’s nest without proper signage.
The Irony of Authorization: When Paperwork Isn’t Enough
This is where the story takes a truly baffling turn. These professionals weren’t operating in the shadows; they had a green light from the very entity they were assessing. Their authorization was not only written but also detailed, explicitly allowing for the methods they employed, including physical entry attempts. Yet, local law enforcement, seemingly unaware or misinformed about the authorized nature of the operation, apprehended them. It’s a stark reminder that even with the best intentions and meticulous planning, a breakdown in communication can have severe, unintended consequences, turning a critical courthouse security assessment into a legal nightmare.
The Long Road to Justice: A Lawsuit and a Significant Payout
What followed their wrongful arrest was a prolonged legal battle. DeMercurio and Wynn didn’t just walk away; they filed a lawsuit against the county, alleging wrongful arrest and defamation. And honestly, can you blame them? Their professional reputations, not to mention their personal freedom, were unjustly compromised. For cybersecurity professionals, an arrest record, even an unwarranted one, can cast a long shadow over their careers.
The Cost of Misunderstanding: A $600,000 Settlement
Fast forward a few years, and the case has finally reached a conclusion. The county agreed to pay Gary DeMercurio and Justin Wynn a substantial sum of $600,000 to settle the lawsuit. This isn’t just a number; it’s a powerful statement. It acknowledges the injustice they faced and underscores the significant legal and financial risks involved when authorized security assessments are mishandled by authorities. For the county, it’s a bitter pill to swallow, but a necessary one to rectify a profound error and ensure that such incidents don’t recur.
Key Takeaways: A Wake-Up Call for the Security Industry and Law Enforcement
This incident is more than just a sensational headline; it offers critical lessons for everyone involved in cybersecurity, law enforcement, and legal frameworks concerning physical penetration testing legal boundaries.
Bridging the Gap: The Crucial Role of Communication
Perhaps the biggest lesson here is the absolute necessity of seamless communication. When high-stakes security assessments, especially those involving physical entry, are undertaken, it’s not enough for the client and the testing firm to be on the same page. Local law enforcement, facility management, and anyone who might encounter the testers in action must be informed and understand the parameters of the exercise. A detailed, multi-party communication plan, perhaps even involving pre-alerting local police forces with contact information and identification protocols, could have prevented this entire ordeal. It’s like planning a massive fire drill: everyone needs to know it’s a drill, not a real emergency.
Protecting Ethical Hackers: The Need for Clear Protocols
This case also shines a spotlight on the vulnerability of ethical hackers. These professionals play a vital role in identifying weaknesses before malicious actors can exploit them. Yet, they often operate in a legal gray area or, as this case demonstrates, can be victims of misinterpretation. There’s a growing need for clearer legal frameworks and industry-wide protocols that protect authorized security testers and ensure their legitimate work isn’t criminalized. How can we encourage vital security work if the professionals doing it fear wrongful arrest?
As the digital and physical worlds continue to converge, the line between ethical security testing and criminal activity can become dangerously blurred without proper safeguards and mutual understanding. This $600,000 settlement is a potent reminder that we all have a role to play in ensuring that those who work to make us safer aren’t penalized for their efforts. This penetration testing lawsuit should serve as a benchmark for future authorized security assessments.
What Are Your Thoughts?
Have you ever encountered similar situations, or do you have strong opinions on the legal protection of ethical hackers? We’d love to hear your perspective on this compelling case. Share your thoughts in the comments below!









